Version 2 of the Remotly Relay Server adds support for TLS and an access password. Even without TLS every connection is end‑to‑end encrypted with RSA-4096 and AES-256; TLS adds a redundant transport layer for strict firewalls at the cost of extra CPU. The access password prevents random users who discover your server's IP and port from using it.
1. Download and unzip
Download the Windows package: remotly‑relay‑windows‑v2.zip. Available builds: remotly‑relay‑windows‑amd64.exe (Windows 64-bit), remotly‑relay‑linux‑arm7 (32-bit ARM), remotly‑relay‑linux‑arm64 (64-bit ARM), remotly‑relay‑linux‑amd64 (Linux 64-bit Intel/AMD).
- RelayGoConfig.json — configuration file
- RelayService.exe — service wrapper that starts the relay executable
- remotly‑relay‑windows‑amd64.exe — the relay server itself (x64 only)
2. Configuration
Non‑TLS configuration:
{
  "tlsEnabled": false,
  "key": "",
  "cert": "",
  "forceTLS": false,
  "domain": "",
  "port": 443,
  "max_bandwidth": 40000000,
  "allowed_bandwidth": 30000000,
  "password": "PasswordPasswordPasswordPassword"
}
TLS configuration (set forceTLS to true to allow only TLS‑encapsulated connections):
{
  "tlsEnabled": true,
  "key": "C:\\relay\\key.pem",
  "cert": "C:\\relay\\fullchain.pem",
  "forceTLS": false,
  "domain": "relay.example.com",
  "port": 443,
  "max_bandwidth": 40000000,
  "allowed_bandwidth": 30000000,
  "password": "PasswordPasswordPasswordPassword"
}- tlsEnabled — enables additional TLS encryption; valid cert and key paths are required when true.
- key — path to the certificate's private key in PEM format. Escape backslashes in JSON (C:\\Path\\key.pem).
- cert — path to the full‑chain certificate in PEM format, same escaping rules.
- forceTLS — when true only TLS 1.2 / 1.3 connections are accepted; both client and host must use TLS.
- domain — domain name assigned to the relay's IP in DNS (recommended, used for SNI).
- port — port used by the relay for communication.
- password — at least 32 characters to restrict access; leave empty to run without a password. A shorter non‑empty password prevents the server from starting.
3. Running the server
Start cmd.exe as administrator and run:
remotly‑relay‑windows‑amd64.exe --config=RelayGoConfig.jsonThen open http://<relay IP>:<port>/connectionTest (or https://<relay domain>:<port>/connectionTest with TLS) in a browser. You should see the message OK.
The process stops when you close the console or restart Windows. To start automatically, copy RelayGoConfig.json, remotly‑relay‑windows‑amd64.exe and RelayService.exe into one folder, open an administrator console in that folder and register the service:
RelayService.exe -install
net start "Remotly Relay Service"

:: to remove
net stop "Remotly Relay Service"
RelayService.exe -remove
4. Registering the relay in your account
Sign in at remotly.com, open Custom Relays and click Add relay server. Provide the IP address, the port(s) from RelayGoConfig.json, a device name visible in the apps, the country code and the same password as in the configuration file.
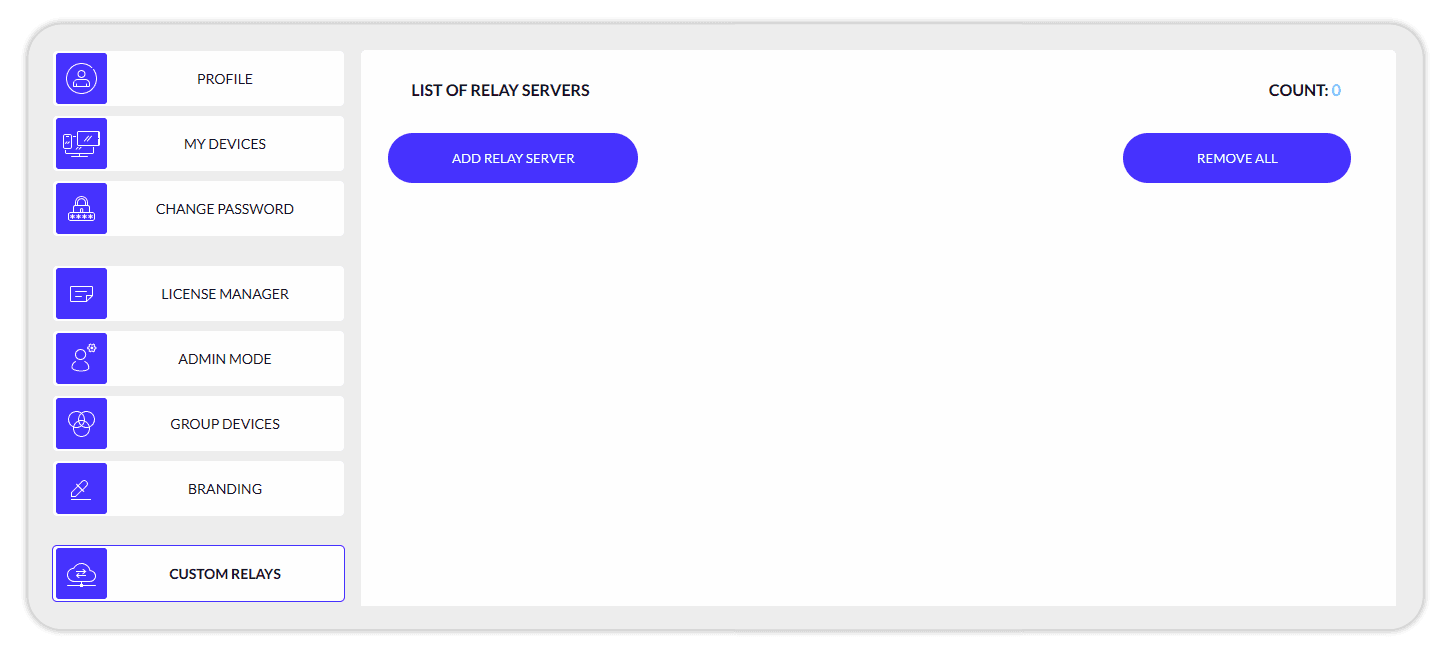
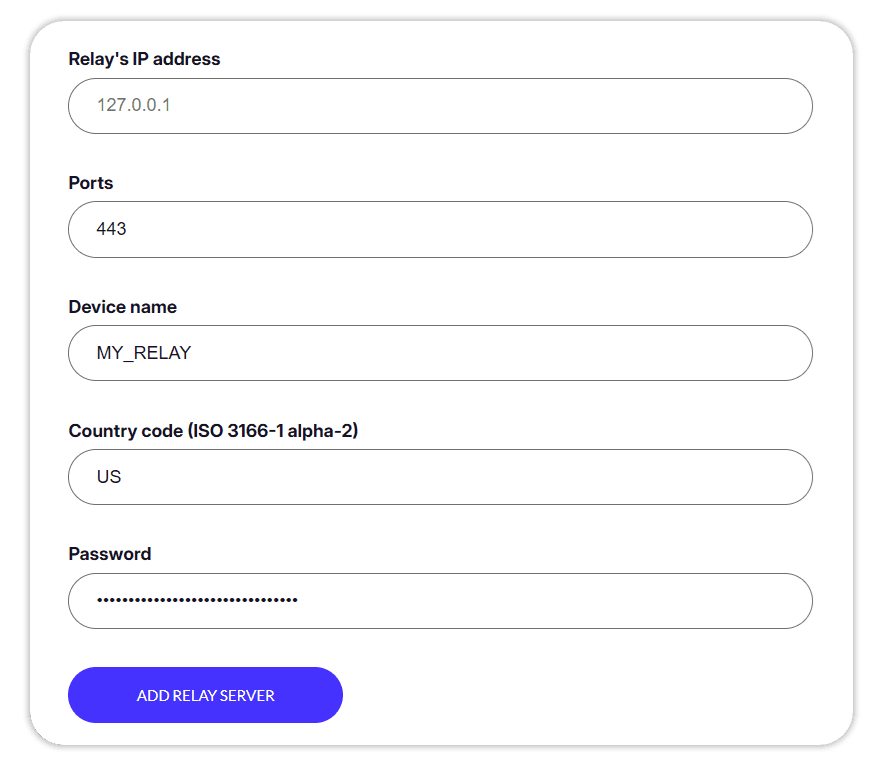
When connecting to another computer with Force Connect Anywhere enabled, you should now see only the country code and name of your private relay.
Troubleshooting
- connectionTest shows OK but relayed connections fail: your server is probably not reachable from outside your network. Configure port forwarding on your public IP and test from an external browser.
- connectionTest shows OK but connections go through an official Remotly relay: you have not added the custom relay to your account in the web panel.
- The relay runs but connectionTest is unreachable: from inside your network, check that the server firewall does not block the relay port; from outside only, fix the port forwarding on your router.